


Authorization Center Mechanism
AuC: Authorization Center Mechanism.
DiDi BNPL is using the JWT_Token authorization mechanism to identify the partner identity.
AuC Work Flow
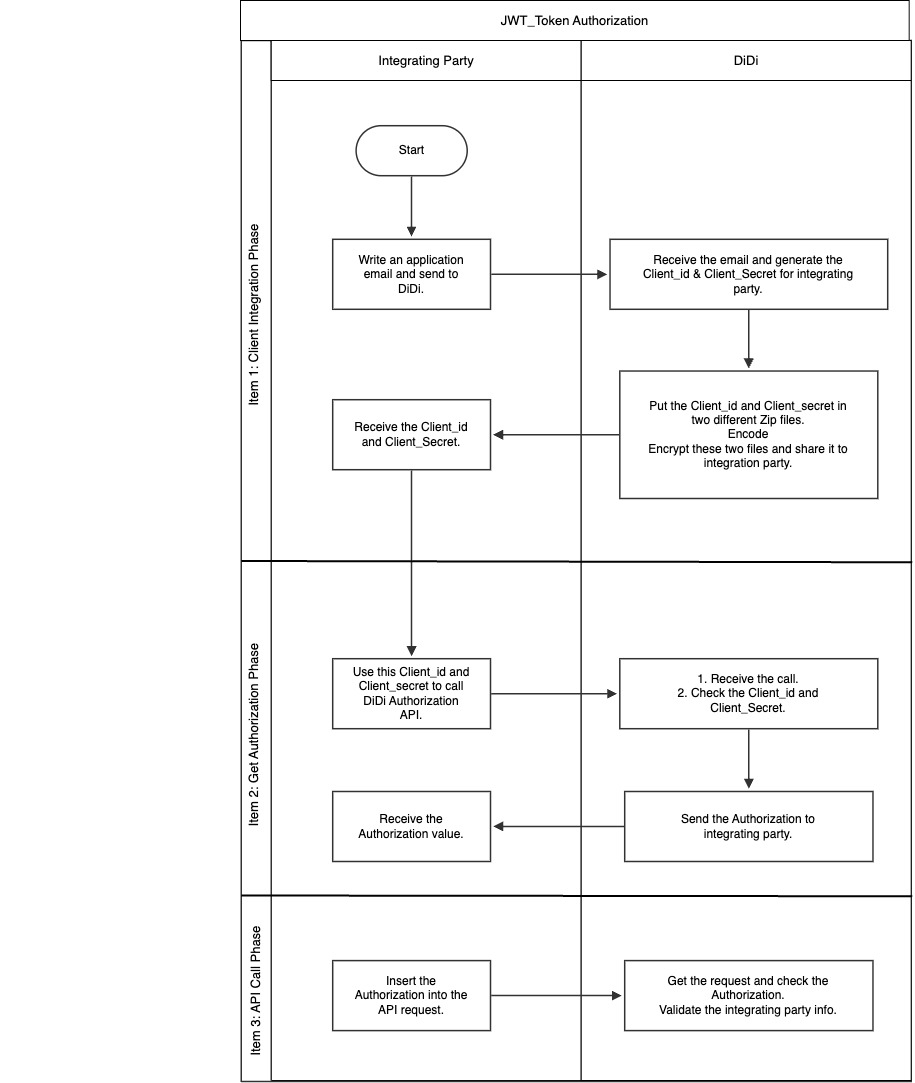
1. Get Secret Phase
The partner should apply to DiDi for the Client_id and Client_secret.
You can get the client_id and client_secret by contacting the DiDi staff through your business (BD) contact.
P.S. If the client_id and client_secret exposed, pls contact the DiDi BD team directly and ask DiDi team:
-
discard the old client_id and client_secret.
-
generate a new client_id and client_secret.
This will be an urgent task for DiDi team. DiDi team will priority it and change it immediately.
2. ACCESS-TOKEN Phase
2.1 The Token Expiration Flow
You should use the POST /external/oauth2/token to get the ACCESS-TOKEN.
This ACCESS-TOKEN will expire in 10 mins. The ACCESS-TOKEN will be always available during this 10 mins whether you generate a new ACCESS-TOKEN or not (valid for 10 mins).
We suggest the integrating party can setup a mechanism to get the next ACCESS-TOKEN within 10 mins, for example 9 mins and 30 seconds.
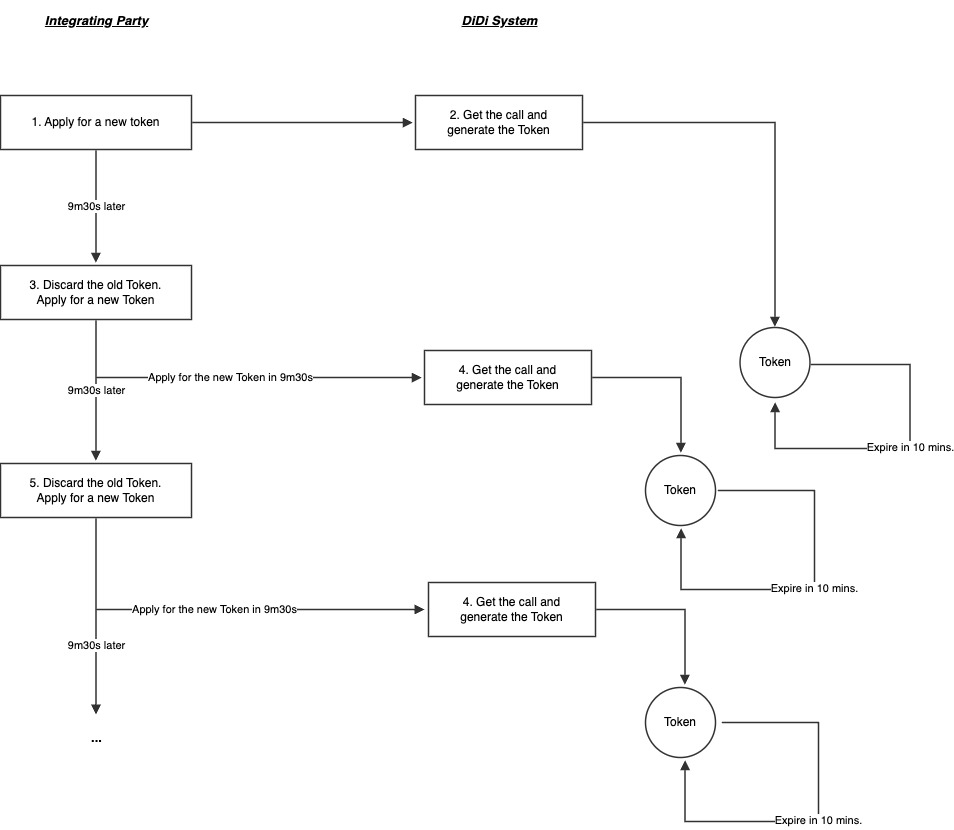
We also contain this logic in this SDK. You can use our SDK to implement this expiration-time control function.
2.2 Token API Request
Path: /external/oauth2/token
Method: POST
Header
Body
2.3 Token API Response
Header
Body
3. API Call Phase
For each API, pls help to insert the access_token into the Authorization field in the header of the request.
For the detail information, pls check the other API specs.